
NIS2 and CER: Why physical security is now becoming a leadership task
News | 3. September 2026.Security starts at the door
The European NIS2 Directive and the complementary CER Directive have a common objective: Increase organisations’ resilience to digital and physical threats. It is not only classic critical infrastructures such as energy supply, healthcare or water management that are affected. Many companies along the supply chain will also need to demonstrate higher security standards in the future. For decision-makers, this means looking at security holistically. After all, even the best IT security strategy loses its effect if sensitive areas such as server rooms, control rooms, technical centres or research zones are not physically adequately protected. The EU CER Directive therefore places greater focus on physical protection.
What does this mean specifically for operators and companies?
NIS2 and CER require affected organisations to carry out a systematic risk analysis and take appropriate protective measures. This includes, among other things, the control of access, traceable authorisation structures, emergency concepts and the complete documentation of security-relevant events.
In practice, this raises key questions:
- Who may enter which zones?
- How quickly can lost access media be blocked?
- Are accesses documented in a tamperproof manner?
- Is access to critical zones guaranteed even during IT or power outages?
- Are existing access systems prepared for current security standards?
Facility managers, technical planners and security officers in particular are therefore facing the challenge of interlinking physical and digital security concepts more closely.
Modern access control as a building block for resilience
A modern access solution can do much more than just open or close doors. In the environment of NIS2 and CER, the following properties are particularly relevant:
- Traceability and auditability: Audit-proof logs enable complete documentation of access events and system events. This facilitates internal controls as well as audits and proof of compliance.
- Protection against tampering: Encrypted communication, modern access media and current security standards help to effectively prevent unauthorised access.
- Quick response: If access media are lost or compromised, they can be blocked at short notice. This significantly reduces potential security risks.
- Business continuity: access to critical zones must also be guaranteed in crisis situations. Offline-capable systems and sophisticated restart concepts support operational readiness even in the event of cyberattacks or system failures.
The EVVA solution approach
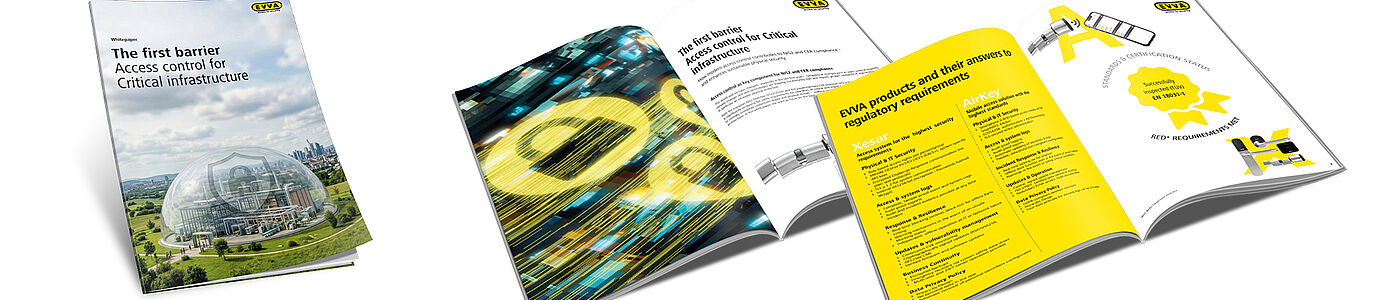
With its modern Xesar and AirKey electronic access systems, EVVA offers solutions that are geared towards current compliance and security requirements. These include role-based permissions, encrypted communication, or disaster recovery concepts. Learn more in our white paper The First Barrier - Access Control for Critical Infrastructure.
How would you like to share?